Patching everything at once can create avoidable downtime, while postponing exposed software leaves risk open. Track component versions, vendor support, internet exposure and known critical fixes; test changes on a copy and schedule a short verification afterward. This guide turns that point into a practical review for a Bangladesh-based team, with checks that can be recorded and repeated.
Start with the real need
Security is a set of repeatable controls, not a single plugin or certificate. Prioritize accounts and systems that could expose customer data or interrupt service, reduce unnecessary access and keep a recovery plan independent of a compromised account. For “Create a Security Patch Priority List for Small Sites”, write down the current state before making a change: the owner, the systems involved, the customer-facing effect and the evidence that would show improvement. This keeps a reasonable idea from becoming an unmeasured change.
A practical workflow
- Patch supported software on a schedule; test important updates before production.
- Keep encrypted, access-controlled backups separate from administrator credentials.
- Record how to report an incident, revoke access and restore service.
- Require MFA for administrators and remove unused accounts and tokens.
- Keep a dated record of the decision, test result, responsible person and rollback or follow-up action.
Plan for Bangladesh-based visitors and teams
Check the experience from the networks and devices your audience actually uses. Make contact, pricing, service limits and next steps easy to find; a desktop test or one successful connection does not represent every visitor. Protect personal information, collect only what the task needs and provide a clear way to request help. Security is a set of repeatable controls, not a single plugin or certificate. Prioritize accounts and systems that could expose customer data or interrupt service, reduce unnecessary access and keep a recovery plan independent of a compromised account.
Measure and improve
Track MFA coverage, overdue critical patches, unresolved findings and time to restore a known-good service. Choose a baseline and a review date before the work begins. If the evidence is mixed, investigate the affected step and record what remains uncertain instead of claiming a result the data cannot support. Recheck after a provider, application or team change.
How BOSS Solution can help
BOSS Solution can discuss hosting and security-related options; confirm included controls and your administration responsibilities. This article is general guidance, not a substitute for provider-specific documentation, legal advice or a security assessment.
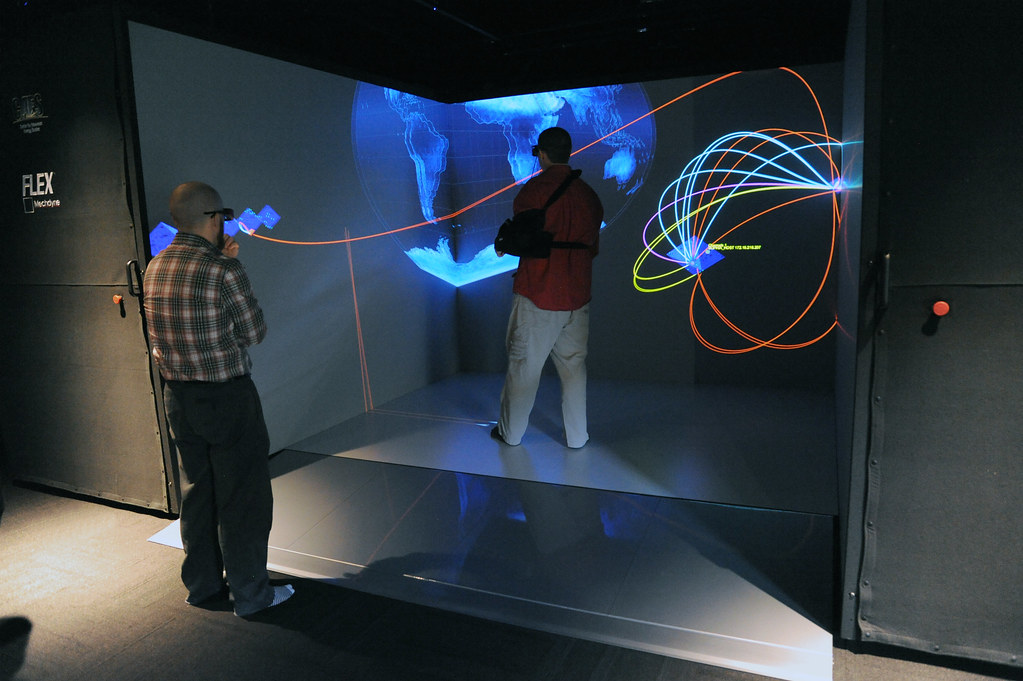
Image credit: "Sophia cybersecurity tool" by Idaho National Laboratory is licensed under CC BY 2.0. To view a copy of this license, visit https://creativecommons.org/licenses/by/2.0/. Source: https://www.flickr.com/photos/30369883@N03/7895744610 License: https://creativecommons.org/licenses/by/2.0/
একসঙ্গে সব patch করলে downtime হতে পারে, আবার উন্মুক্ত software পিছিয়ে রাখলে ঝুঁকি থাকে। component version, vendor support, internet exposure ও জরুরি fix লিখুন; copy-তে পরীক্ষা করে পরে সংক্ষিপ্ত verification নির্ধারণ করুন। এই নির্দেশিকায় বিষয়টিকে বাংলাদেশের একটি দলের জন্য ব্যবহারিক পর্যালোচনায় রূপ দেওয়া হয়েছে, যাতে যাচাইগুলো নথিভুক্ত ও পুনরাবৃত্তি করা যায়।
Start with the real need
নিরাপত্তা পুনরাবৃত্তিযোগ্য control-এর সমষ্টি; একটি plugin বা certificate-ই সব নয়। customer data প্রকাশ বা service বন্ধ করতে পারে এমন account ও system-কে অগ্রাধিকার দিন, অপ্রয়োজনীয় access কমান এবং আক্রান্ত account-এর ওপর নির্ভরশীল নয় এমন recovery plan রাখুন। “ছোট website-এর security patch অগ্রাধিকার তালিকা” বিষয়ে পরিবর্তনের আগে বর্তমান অবস্থা লিখুন: দায়িত্বপ্রাপ্ত ব্যক্তি, সংশ্লিষ্ট system, গ্রাহকের ওপর প্রভাব এবং উন্নতি বোঝার প্রমাণ। এতে ভালো ধারণাও পরিমাপহীন পরিবর্তনে পরিণত হবে না।
A practical workflow
- সময়সূচি অনুযায়ী supported software patch করুন; production-এর আগে গুরুত্বপূর্ণ update পরীক্ষা করুন।
- administrator credential থেকে আলাদা access-controlled encrypted backup রাখুন।
- incident report, access revoke এবং service restore করার পদ্ধতি লিখুন।
- administrator account-এ MFA চালু করুন এবং অব্যবহৃত account ও token সরান।
- সিদ্ধান্ত, পরীক্ষার ফল, দায়িত্বপ্রাপ্ত ব্যক্তি এবং rollback বা follow-up কাজের তারিখসহ নথি রাখুন।
Plan for Bangladesh-based visitors and teams
আপনার audience যে network ও device ব্যবহার করে, সেখান থেকে অভিজ্ঞতা যাচাই করুন। যোগাযোগ, মূল্য, সেবার সীমা ও পরবর্তী ধাপ সহজে খুঁজে পাওয়ার ব্যবস্থা রাখুন; desktop-এ সফল পরীক্ষা সবার অভিজ্ঞতা ধরে নেওয়া যায় না। ব্যক্তিগত তথ্য সুরক্ষিত রাখুন, কাজের জন্য প্রয়োজনীয় তথ্যই সংগ্রহ করুন এবং সহায়তা চাওয়ার স্পষ্ট উপায় দিন। নিরাপত্তা পুনরাবৃত্তিযোগ্য control-এর সমষ্টি; একটি plugin বা certificate-ই সব নয়। customer data প্রকাশ বা service বন্ধ করতে পারে এমন account ও system-কে অগ্রাধিকার দিন, অপ্রয়োজনীয় access কমান এবং আক্রান্ত account-এর ওপর নির্ভরশীল নয় এমন recovery plan রাখুন।
Measure and improve
MFA coverage, মেয়াদোত্তীর্ণ গুরুত্বপূর্ণ patch, অমীমাংসিত finding এবং service restore-এর সময় দেখুন। কাজ শুরুর আগেই baseline ও review date ঠিক করুন। ফল মিশ্র হলে সমস্যার ধাপ অনুসন্ধান করুন; তথ্য সমর্থন করে না এমন দাবি না করে অনিশ্চয়তা নথিভুক্ত করুন। provider, application বা দলের পরিবর্তনের পর আবার যাচাই করুন।
How BOSS Solution can help
BOSS Solution-এর hosting ও security-সম্পর্কিত বিকল্প আলোচনা করা যায়; অন্তর্ভুক্ত control ও administration-এর দায়িত্ব যাচাই করুন। এই লেখা সাধারণ নির্দেশনা; provider-এর documentation, আইনি পরামর্শ বা security assessment-এর বিকল্প নয়।
ছবির স্বীকৃতি: "Sophia cybersecurity tool" by Idaho National Laboratory is licensed under CC BY 2.0. To view a copy of this license, visit https://creativecommons.org/licenses/by/2.0/. উৎস: https://www.flickr.com/photos/30369883@N03/7895744610 লাইসেন্স: https://creativecommons.org/licenses/by/2.0/